One scan in. Two assessments out.
Each Lab reads your findings and returns an executive-grade verdict — then exports it as a branded, auditor-ready PDF.
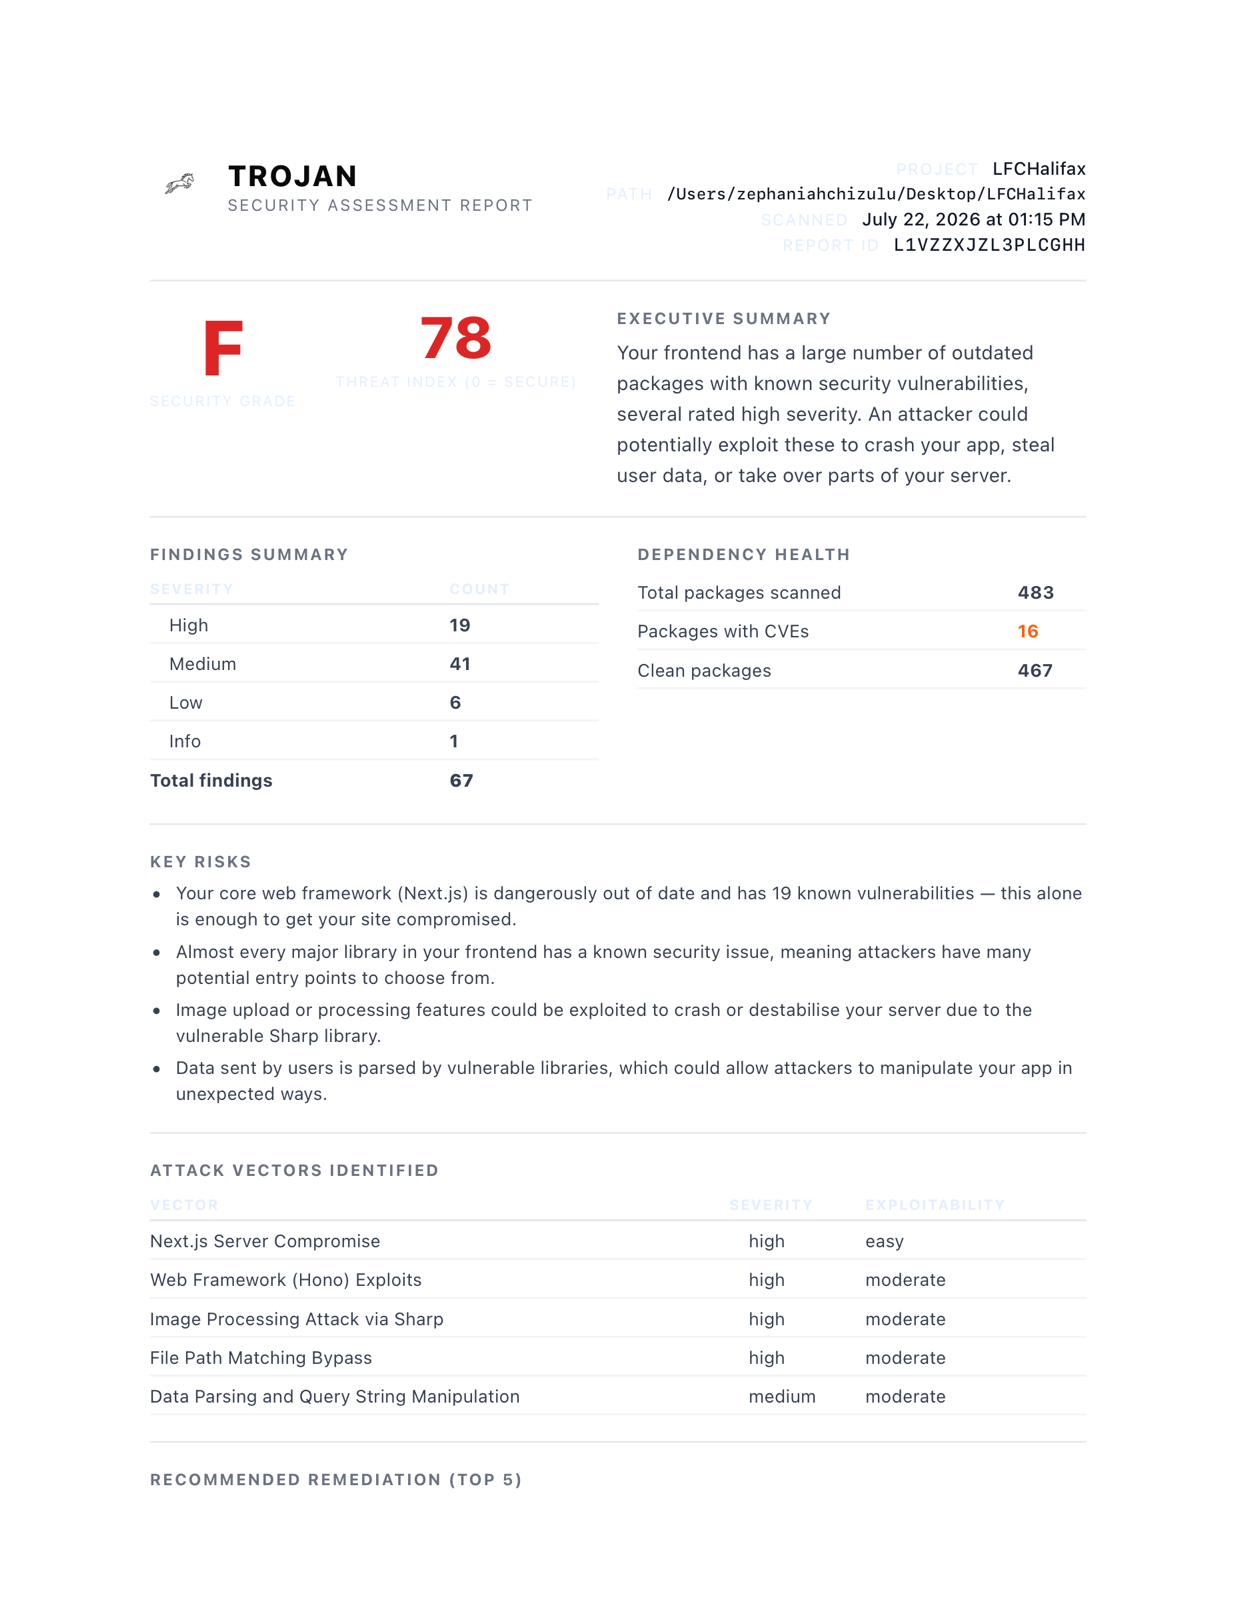
Security Assessment
Runs your findings through Claude to build an attacker's-perspective threat model — what actually chains together, and what to fix first.
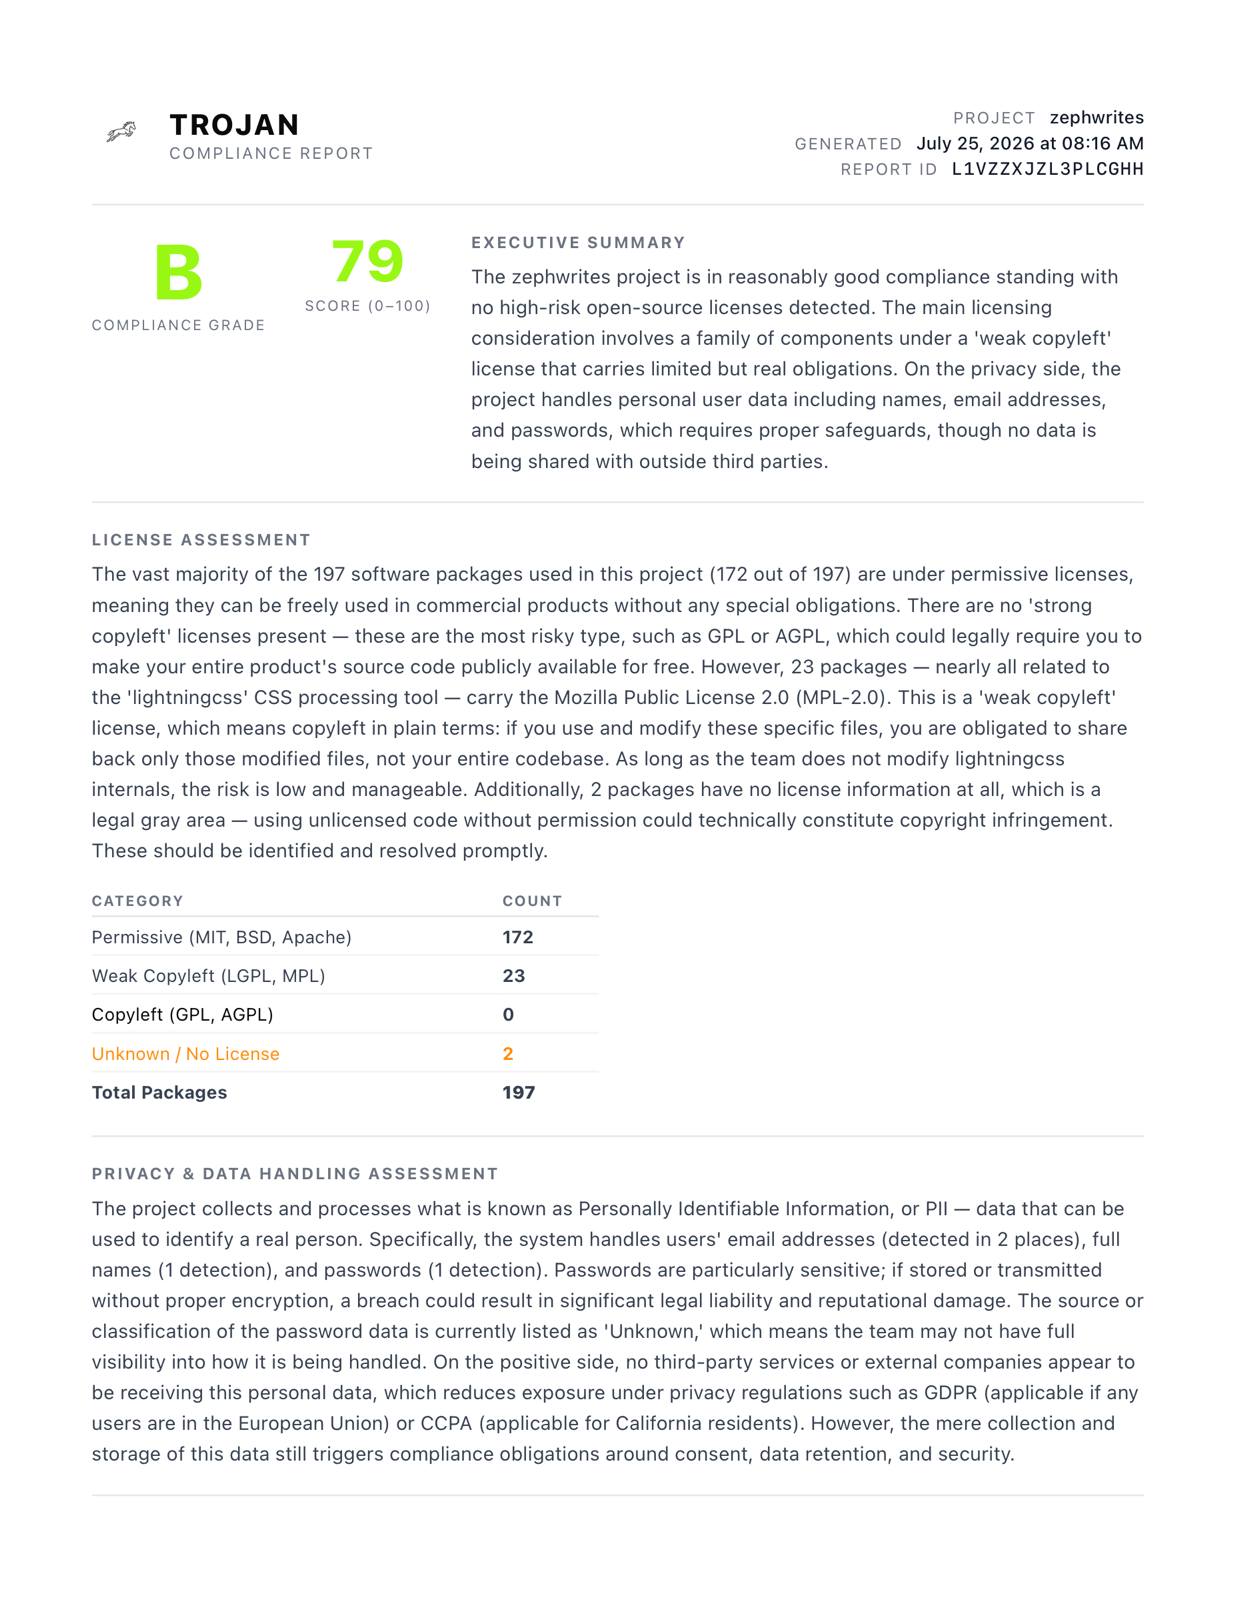
Compliance Report
Combines license analysis with privacy & data-flow analysis into one assessment — the legal and regulatory picture, in plain English.
The output looks
like it cost $5,000.
A branded certificate — grade badge, executive summary, the findings that matter, a unique Report ID and a QR code back to trojancli.com. Hand it to anyone.
trojancli.com
Three findings chain into a plausible account-takeover path: a hardcoded credential grants a foothold, an unrate-limited login enables credential stuffing, and an outdated dependency exposes a known RCE. Individually moderate; together, a critical path. Priority fixes below close it in under a day.
| Vector | Severity | Exploit |
|---|---|---|
| Credential → account takeover | Easy | |
| SQL injection via user input | Moderate | |
| Outdated lodash — known CVE | Hard |
Illustrative Security Assessment. The Compliance Report follows the same certificate format with a license-risk table and privacy assessment.
One document, many rooms.
Hand over a dated, ID'd assessment that maps to SOC 2 and OWASP — no screen-share required.
Prove your code is safe before you ship it to them. A branded PDF closes the security-review loop.
Answer the vendor security questionnaire with a document instead of a spreadsheet.
Give the board a grade and a verdict they can read in a minute — not a raw findings dump.
Scanning runs on your machine. Only an anonymized findings summary is sent for AI synthesis — never your code.
Claude turns raw findings into a plain-language verdict a founder — and their board — can actually act on.
Every Lab exports a branded, auditor-ready certificate with a Report ID and QR code — ready to send.